Skip to content

Security and data protection Protection is the database’s job, not the application’s.

The data a property management holds is people’s names, phone numbers, units and debts. In MeskenPlus the most critical rules are not enforced by hiding things in the interface but by making them mandatory in the database.

Features labeled “On the roadmap” are in development; the others can be used today.

Isolation
Row level, in the database
Records
Never deleted, linked by a hash chain
Sign-in
Two-step verification for management roles

The controls on screen

The rules live in the database; their result shows in the panel, in the records themselves. The screens use the data of the demo property Huzur Sitesi.

A trail for every action

Every record, display of personal data and export in a property: who did what, when, and with what result. The audit trail cannot be changed or deleted.

  • For master data, the value before and after is kept field by field.
  • Personal data access and failed actions can be filtered separately.
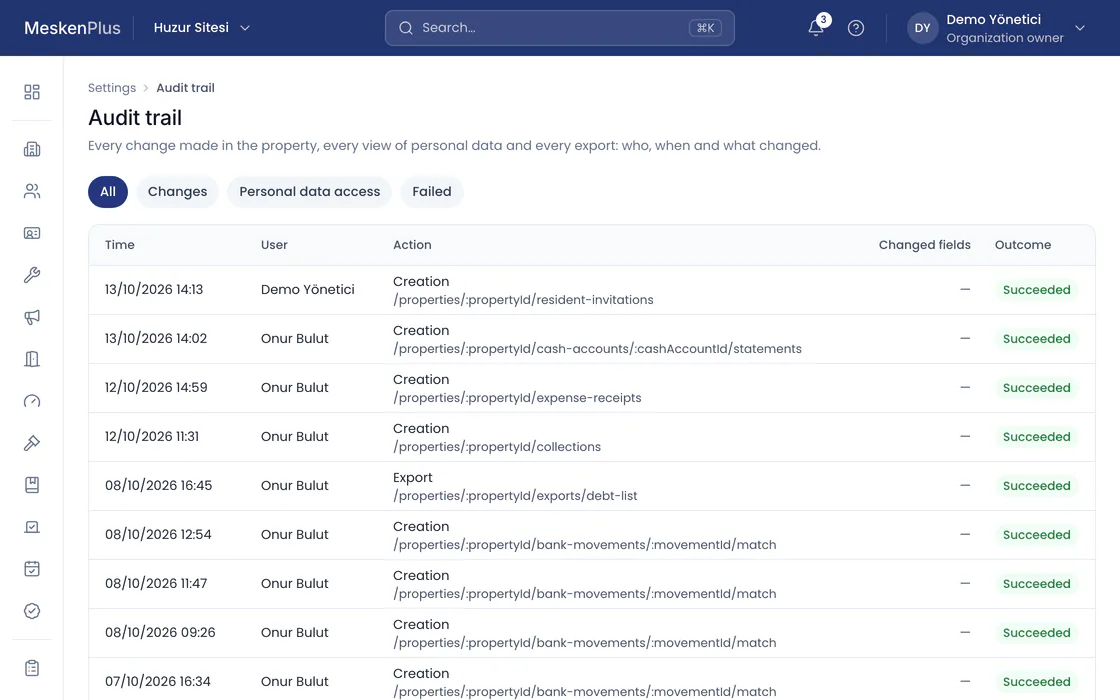
The audit trail in the MeskenPlus panel: every record and export made in the property with its time, user, action and result; changes, personal data access and failed actions can be filtered separately.
Demo data · Huzur Sitesi · Audit trail

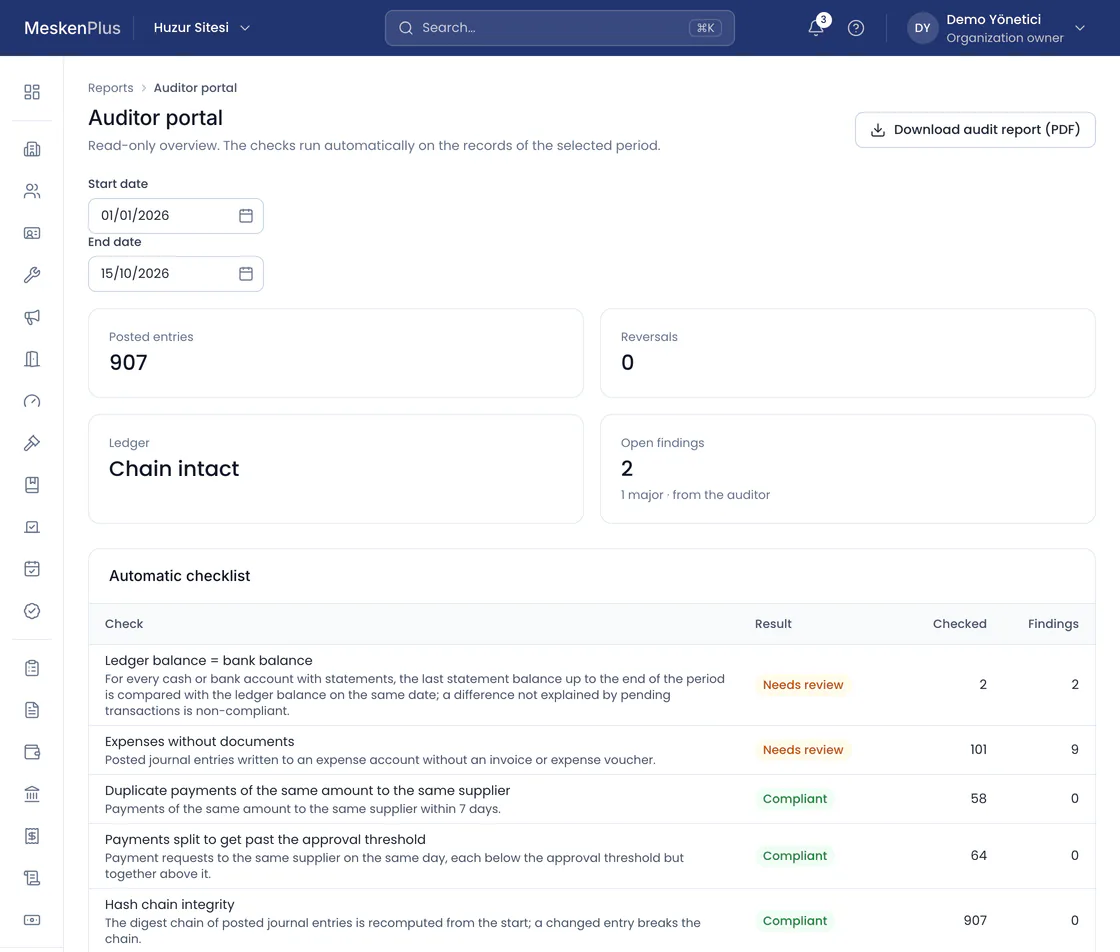
Auditors check the records themselves

The auditor signs in read-only. The portal checks the hash chain, ledger–bank agreement, expenses without documents, duplicate payments and payments split under the approval threshold on the records.

  • The auditor can only write findings and cannot change any other record; this rule is enforced in the database too.
  • The standard audit report downloads as a PDF.
The auditor portal in the MeskenPlus panel: the number of posted journal entries and reversals, the ledger’s hash chain intact; the automatic checklist with ledger–bank agreement, expenses without documents, duplicate payments, payments split under the approval threshold and the hash chain, each with its result.
Demo data · Huzur Sitesi · Auditor portal

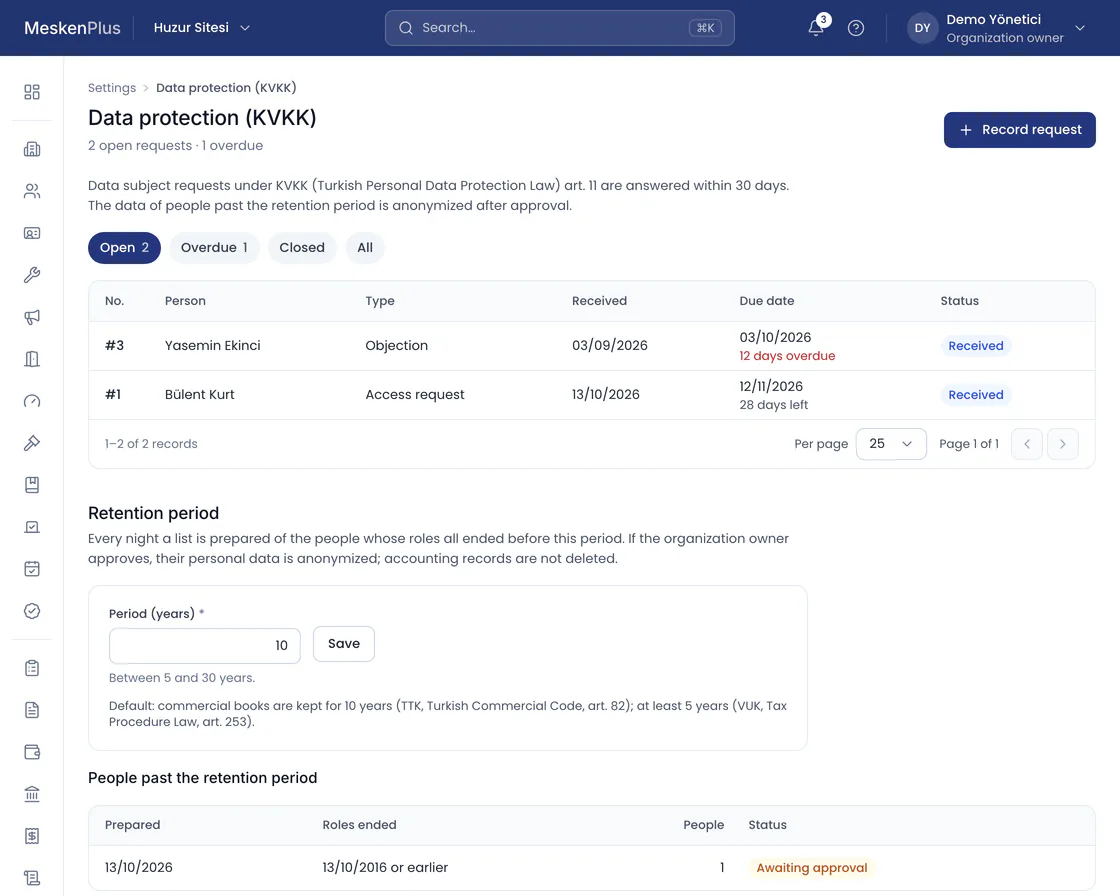
KVKK requests on time

Requests from data subjects under KVKK (Turkish Personal Data Protection Law) to access, correct, delete or object are tracked against the 30-day legal deadline; a request past its deadline is flagged.

  • The personal data of people whose retention period has ended is anonymized with the organization owner’s approval; accounting records are not deleted.
  • A person’s data report is prepared as PDF or JSON.
The KVKK (Turkish Personal Data Protection Law) screen in the MeskenPlus panel: data subject requests with their type, date received, 30-day deadline and status; retention periods and the pending anonymization of people whose retention period has ended.
Demo data · Huzur Sitesi · KVKK requests

Who sees what?

Permissions are given with a role, a scope and a validity date: organization, property, section or block. A job title is not a permission.

Access by role and scope
RoleSeesDoesTwo-step verification
Organization ownerAll of the organization’s propertiesEverything; team, permissions and KVKK requestsRequired
Property managerThe properties in their scopeBudgets, charges, collections, expenses and approvalsRequired
AccountantLedger, reports and peopleJournal entries, charges, collections, expenses and payrollRequired
Block or section managerOnly the units and people of their own block or section; not the ledgerResident invitations, service requests, meter readingsOptional
AuditorLedger, records and audit trailOnly writes findingsRequired
Board memberLedger, budgets and decisionsTakes part in payment approval; cannot pay aloneOptional
Owner, tenant and residentOnly their own unit and their own periodDebts and receipts, announcements, polls, service requests; household members do not see debtsOptional
MeskenPlus teamOrganizations’ metadataNo permission on the people, journal entry and document tablesAlways required
Seeing personal data in full is a separate permission: it is revealed field by field and written to the audit trail.

Isolation between organizations

Each organization’s data sits in the same database, isolated from the others.

  • Row-level security

    A row-level security rule runs on every table that belongs to an organization. The application connects with a separate database role that cannot bypass it.

  • Fails closed

    If the request context has not been set, a query sees no rows at all; an error leads to an empty result, not to a data leak.

  • The platform does not see content

    The MeskenPlus team’s administration tool sees organizations’ metadata; it has no permission on the people, journal entry and document tables.

Record integrity

Accounting records and the audit trail cannot be changed afterwards.

  • Journal entries that cannot be deleted

    Updating or deleting posted journal entries and their lines is blocked by a database trigger. Corrections are made by reversal.

  • Hash chain

    Every journal entry carries a hash of the one before it; inserting a record in between or changing one shows up in the chain check.

  • Audit trail

    Management actions are written to a table that cannot be changed, with who, what, when, from which address and the result.

Account security

Sessions are short-lived; the browser never connects to the API directly.

  • Account lockout and request limits

    After repeated wrong passwords the account is locked for a while; a request limit applies per address.

  • Secure sessions

    A short-lived access token, and a refresh token in a cookie only the server can read.

  • Two-step verification

    Required for the organization owner, property manager, accountant and auditor roles; with single-use recovery codes and a list of sessions.

  • Extra approval when money leaves

    On the roadmap

    Approval with a one-time code, and a notification, for payments and changes to bank details.

KVKK principles

The property management is the data controller; MeskenPlus, as data processor, processes data only on the management’s instructions.

  • Debt privacy

    Debtors’ names, units and debts are never shown on a shared screen, notice board, bulk message or PDF.

  • Consent records

    At sign-up, the terms of use and the privacy notice are accepted with their version number and stored; commercial message consent is separate and optional.

  • Field-level encryption

    Turkish ID numbers, phone numbers and IBANs are stored encrypted and masked on screen; revealing the full value requires a permission and is written to the audit trail.

  • Request tracking

    A person’s access and deletion requests are tracked against their legal deadline; accounting records are not deleted, personal fields are anonymized at the end of the retention period.

Money never stops with us

Payments are made into the property’s own bank account. MeskenPlus does not collect, hold or pay out money; it only reads the transaction data. So the property’s money is never exposed to a third party’s risk.

How transactions arrive from the bank
Sample data

Questions about security

Where is the data stored?

The servers are in data centres in Türkiye. Each organization’s data is isolated at row level in the database; Turkish ID numbers, phone numbers and IBANs are stored encrypted.

Can MeskenPlus staff see our data?

No. The platform administration tool sees organizations’ metadata (organization, license, user account); it has no permission in the database on the people, journal entry and document tables.

Can a record be deleted?

Posted accounting records and the audit trail are never deleted or changed; corrections are made by reversal, with the reason and who made it. Personal data is anonymized with approval at the end of the retention period.

What if my password is stolen?

In management roles, signing in also needs a 6-digit code sent to your email or made by an authenticator app, and the account is locked after repeated wrong attempts. You can end sessions on other devices from “My sessions”; when the password changes, every session other than the current browser is ended.

How are files with personal data protected?

Only authorized roles can export personal data; every page of the file is watermarked with the user and the time, and the export is written to the audit trail with the file’s hash.

Let us go through your requirements on the records.

Bring your security and KVKK questions to a demo, and we will look at them together on the panel’s own screens.